
SOC 2 · ISO 27001 readiness
Audit readiness, with the evidence to back it.
Track controls, evidence that expires, policies, risks and vendors in one workspace, with readiness computed live from your own records. Trust doesn't certify anyone — it keeps the work organised and exportable for your auditor.
Free and open source (AGPL-3.0).
- SOC 2
- CC1–CC9 · 33
- ISO 27001
- Annex A · 15
- Export
- JSON · package
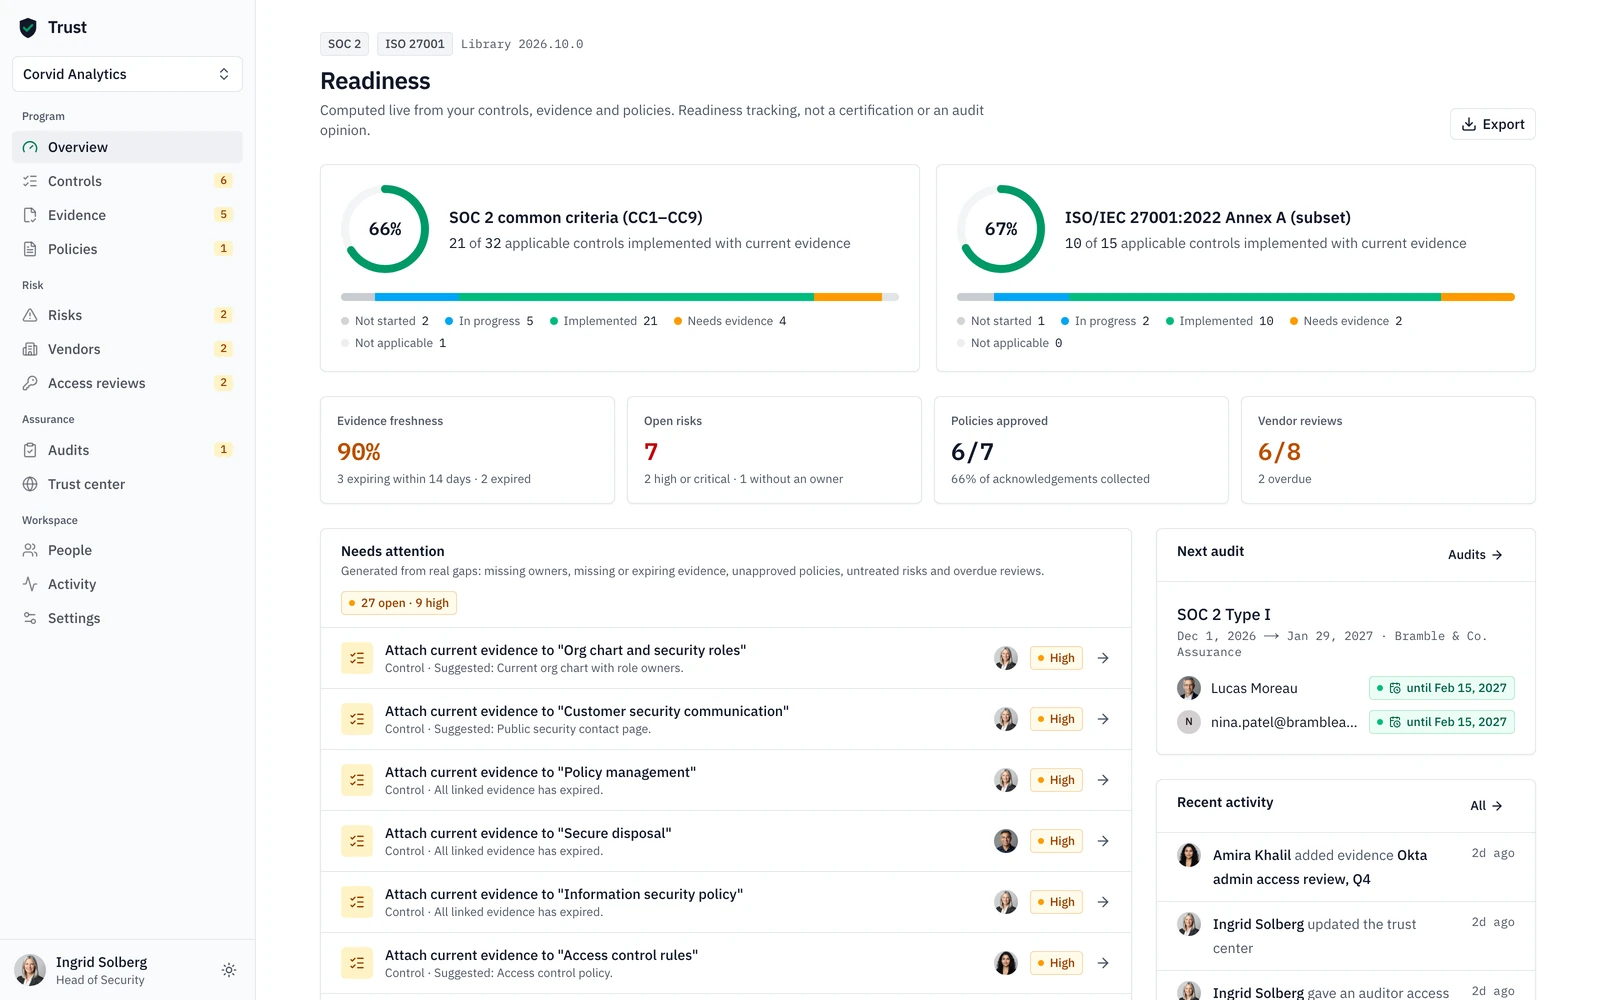
controls / evidence / policies
The whole readiness program in one workspace
Every figure on the dashboard is computed from your records, with its definition on screen.
A versioned control library
SOC 2 common criteria (CC1–CC9, 33 controls) and an ISO 27001:2022 Annex A subset (15 controls), paraphrased and mapped. Not applicable needs a written reason.
Evidence that expires
Attach a link or pasted text with a collection date, review cadence or expiry. When it lapses, its controls show “needs evidence” on their own.
Policies with versions
Start from eight templates. Edits create versions, approved text is never rewritten, and acknowledgement coverage is measured.
Risks and vendors
Score risks on a 5×5 heat map; accepting one needs a rationale. Keep a tiered vendor inventory with overdue reviews flagged.
Audit periods and findings
Give an auditor read-only access until a date — after it, the server refuses. Track findings through remediation.
Quarterly access reviews
List critical systems and their users, sign off each quarter, and record who was kept and who was removed.
A trust center you control
Off by default. Publish only what you choose: frameworks, readiness, per-category counts and approved policy names.
Gap tasks from real gaps
Missing owners, expiring evidence, unapproved policies, untreated high risks and overdue vendors, in priority order.
how it works
From framework to evidence package
One action endpoint per workspace: every change passes the same role check and lands in the audit log.
Pick your frameworks
Choose SOC 2, ISO 27001 or both from the built-in library, pinned to a version. Library updates arrive as an explicit, audited diff.
Assign controls, attach evidence
Give every control an owner and attach evidence with its collection date and review cadence. Owners and admins accept or reject it.
Close the gaps
Work the generated task list: approve policies, refresh expiring evidence, treat high risks, review vendors and access.
Hand over to your auditor
Open an audit period with read-only access and export an evidence package per framework: requirement → controls → evidence.
plain language
What Trust is not
Compliance tools are easy to over-sell. Here is exactly where Trust stops, so nobody on your team is surprised in front of an auditor.
Not a certification
Trust never says you are compliant. Readiness figures are computed from your own records, and the public page labels them as self-reported.
Not your auditor
An independent audit firm examines your controls and issues the report. Trust keeps their requests, findings and evidence organised.
Not automated monitoring — yet
There are no cloud or identity connectors and no automated checks today. Your team records evidence and its dates.
No file uploads yet
Evidence is a link or pasted text. File storage isn't connected, and the app says so where you'd expect an upload.
open source
Your evidence graph stays yours
Trust is free and open source under the AGPL-3.0. Your whole program exports as versioned JSON whenever you want — no support ticket required.
Full export and evidence package
The workspace as versioned JSON, plus an audit-ready package per framework with dates and freshness.
Append-only activity
Every change goes to the audit log, visible to your team under Team & activity.
Least-privilege roles
Owners, admins, members and read-only viewers — suited to auditors — checked on the server for every action.
Code you can audit
The full source is public, including exactly how coverage and freshness are calculated.
faq
What security teams ask
See where your program really stands
Create a workspace, pick a framework and assign your first controls.
Start your program